
Planning your communications only after an attack has occurred is an extremely risky approach. Experience shows that a data breach or ransomware attack does not give an organisation the time to calmly craft a message from scratch. Consequently, when a crisis strikes, every minute counts, and the lack of a ready-made action plan inevitably leads to paralysing chaos.
As a result, PR and marketing departments must build up their crisis preparedness well in advance. Furthermore, since an incident directly impacts a company’s image and trust, the communications team should be involved in the preparations on an equal footing with IT experts and senior management. Consequently, only by working together in advance can a brand’s reputation be effectively protected when the moment of truth arrives.
Why PR and marketing must be prepared before an incident occurs
Following a data breach, a company usually takes action on several fronts simultaneously:
- technical,
- operational,
- legal,
- regulatory,
- and communication
Each of these areas has its own priorities, time pressures and risks. The problem is that, without prior preparation, the organisation starts to improvise precisely when it should be following a plan.
For PR and marketing departments, a lack of preparation usually means:
- delayed communication,
- inconsistent messages,
- a lack of clear roles,
- language that is too technical or too cautious,
- and a loss of control over the narrative.
Companies that weather a cyber crisis well are not usually better simply because they have never been attacked. They are better because they have prepared in advance, including in terms of communication.
What the PR and marketing departments need to understand about data breaches
To be well prepared for a crisis, the communications team does not need to be an expert in security architecture. However, it should understand a few basic principles.
A data breach is not just a legal issue
Admittedly, there are regulatory, notification and formal obligations. But from a reputational perspective, it is above all a situation that undermines the trust of customers, partners and the market.
In a crisis, you can’t afford to wait for the full picture
This is one of the most important lessons. In the hours immediately following an incident, much of the information will be incomplete. This is to be expected. However, a lack of full information does not absolve the company of its responsibility to communicate early and honestly.
Communication following an incident has an impact on the extent of reputational damage
The brand is not judged solely on the basis of the leak itself. It is also judged on the following:
- how quickly reacted,
- as clearly stated,
- whether managed to remain consistent,
- and whether it took its audience seriously.
Where to start when setting up a PR and marketing department
The most important step is to stop treating a cyber crisis as an abstract scenario for ‘some time in the future’. As long as there is no one in charge of the issue and no specific action plan in place, it tends to be sidelined.
In practice, it’s a good idea to start with four questions:
- what types of incidents could realistically affect our organisation,
- which groups would be covered by them,
- what communication channels would we need to set up,
- who actually makes communication decisions under time pressure.
These questions help you move from thinking about the crisis in general terms to a concrete plan of action.
Element 1: crisis scenario map
The PR and marketing department should be aware that not every incident requires the same approach to communication. The situation is different when it comes to:
- a customer data breach,
- ransomware and service outages,
- hacking of social media accounts,
- a leak of employee data,
- vulnerability disclosure,
- or an incident affecting business partners.
Each of these scenarios raises different questions, evokes different emotions and carries a different level of reputational risk.
Therefore, the first step should be to draw up a list of potential incidents along with the corresponding responses:
- who might be affected,
- what will be afraid of,
- what information will be required,
- and which communication channels will be key.
Element 2: a clear division of roles and responsibilities
One of the most common causes of chaos following an incident is not the lack of communication itself, but the lack of clarity as to who is responsible for it.
In a well-run organisation, the team knows:
- who collects and verifies technical information,
- who decides whether the message is released to the public,
- who is drafting the document,
- who approves the content,
- who is responsible for the media,
- who represents the clients,
- who is in charge of social media,
- who communicates with staff,
- and who is authorised to make public statements.
Without this, every minute of the crisis is wasted trying to work out ‘who should do it now’.
A minimum that is worth setting in advance
In practice, it is a good idea to have a simple responsibility matrix set out in writing, covering:
- security / IT – source of information about the incident,
- legal / compliance – assessment of formal obligations,
- PR / communications – drafting press releases and managing communications,
- marketing / digital – owned channels, website, email marketing, social media,
- management – strategic decisions and high-level presentations.
Element 3: ready-made holding statements and draft messages
One of the most practical preparatory steps is to create a set of draft messages that can be quickly adapted to a specific incident.
These shouldn’t be definitive statements written once and for all. Rather, they are ready-made frameworks that allow you to act quickly without having to write everything from scratch.
It is worth preparing sketches for situations such as:
- the incident has been detected and is currently being analysed,
- confirmed data breach,
- temporary unavailability of services,
- a message to customers containing instructions,
- response to the media,
- internal memo to staff.
This means the team doesn’t have to start from scratch at the worst possible moment.
Element 4: a list of stakeholders and their information needs,
One of the biggest mistakes in post-cyberincident communication is treating all audiences the same. Yet each group has different needs.
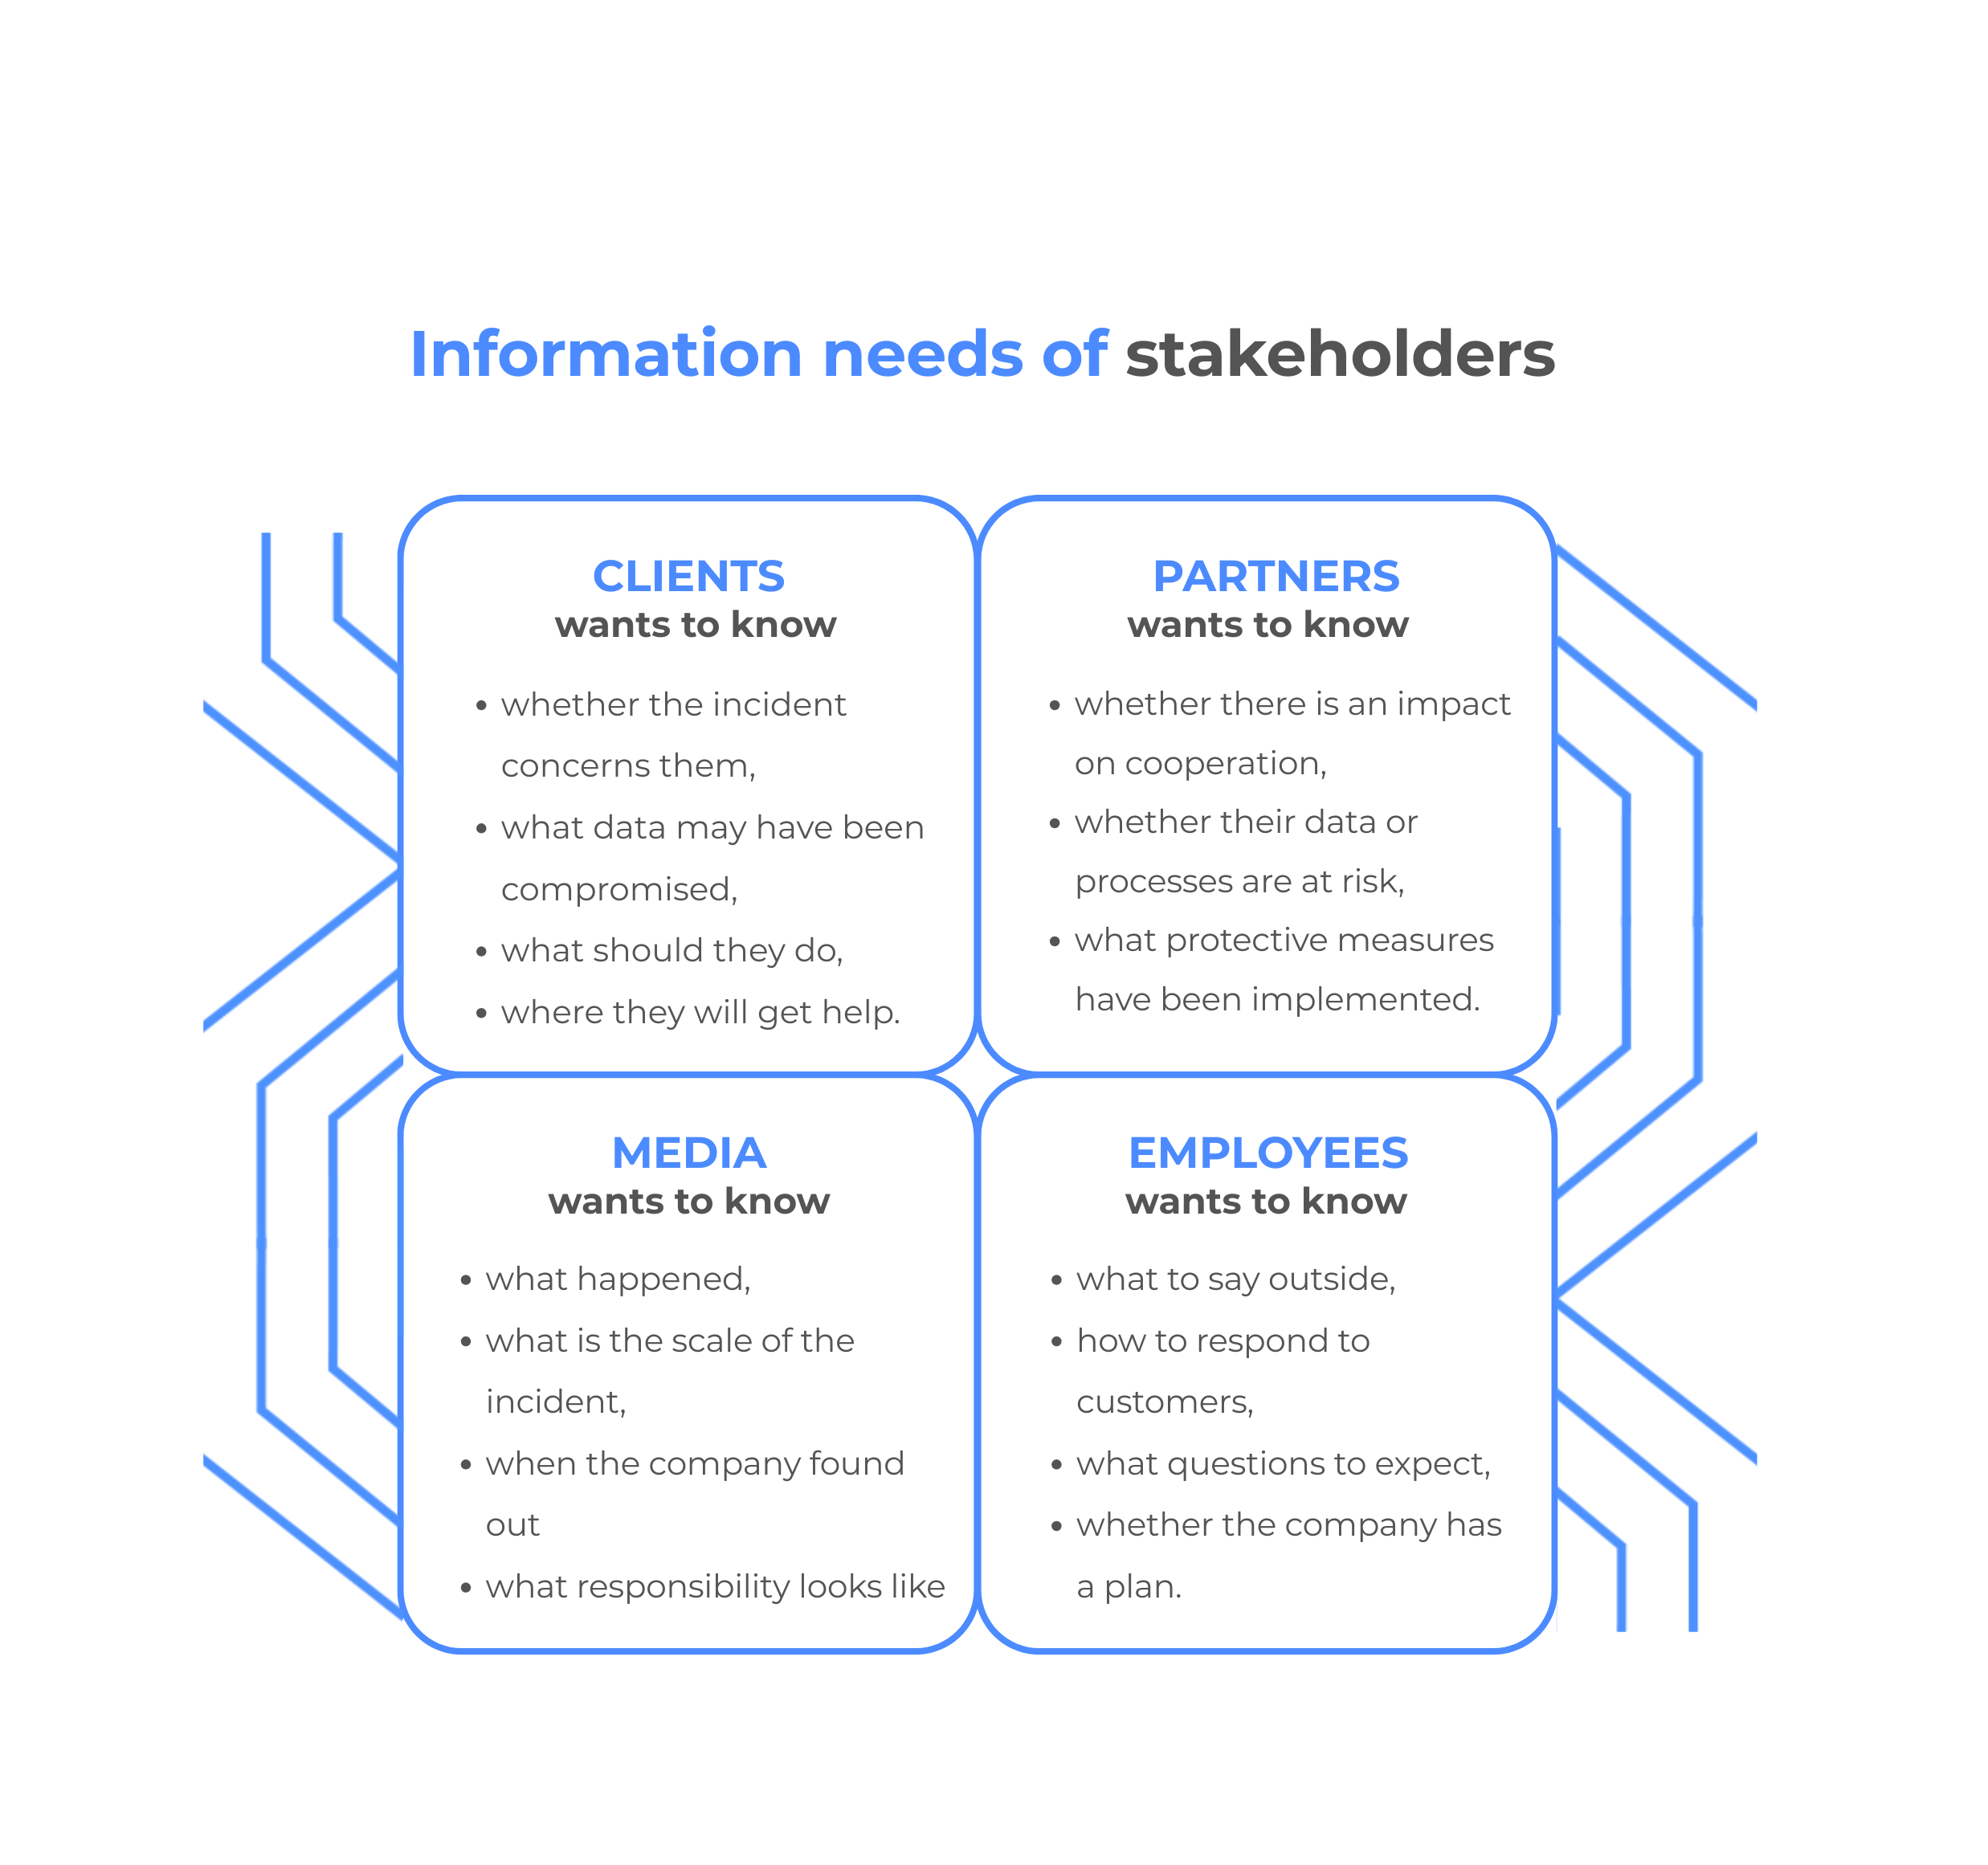
The PR and marketing department should have a pre-prepared map of these groups and a basic communication framework for each of them.
Element 5: Communication procedure during the first 24–48 hours
This is probably the most important part of the preparation. In the first few hours after an incident, the team should not have to wonder where to start. They should have a simple, familiar plan.
Such a plan may include:
The first few hours
- gathering basic information from security/IT,
- activation of the crisis management team,
- identifying the owner of the communication,
- preparation of the preliminary position.
6–12 hours
- assessment of the impact on customers and services,
- drafting the initial statement or holding statement,
- agreeing on a standard response for customer service and staff.
12–24 hours
- the publication of the announcement via the relevant channels,
- preparation of Q&A,
- monitoring of media and social media reactions,
- plan for future updates.
24-48 hours
- clarification of the information,
- updates to announcements,
- przygotowanie odpowiedzi na najczęściej pojawiające się pytania,
- support from the board and spokespersons.
The simpler and more practical the procedure, the greater the chance that it will actually be used.
Element 6: Exercises and test scenarios
The biggest mistake is to assume that the document itself is enough. Even a well-written contingency plan won’t work if no one has tested it in practice beforehand.
The PR and marketing department should therefore take part in scenario-based exercises alongside:
- security,
- IT,
- legal,
- compliance,
- the management,
- and customer service.
Exercises like these help answer very specific questions:
- do we know who initiates the communication,
- can we prepare a message quickly,
- does our approval process operate under time pressure,
- do we know who is responsible for the media,
- are our channels ready for immediate action?
Practical exercises very quickly reveal gaps that aren’t apparent at the theoretical level.
Element 7: preparing communication channels and resources
During a cyber crisis, it is not only the content that matters, but also the ability to publish it quickly. The marketing and communications department should check the following in advance:
- who has access to the website and can update the message quickly,
- who is responsible for sending emails to customers,
- who has access to social media profiles,
- who manages the FAQ section or help centre,
- who supports the customer service team with pre-prepared responses.
This is a very practical aspect that is often overlooked. Yet even the best message won’t help if the organisation is unable to publish it quickly and consistently enough.
What skills are most important today for PR and marketing in a cyber crisis?
The point is not for every marketer or PR specialist to become a cybersecurity expert. The point is to develop a few key skills that are crucial in a crisis.
The most important of these are:
- the ability to explain complex topics in simple terms,
- understanding the mechanics of a reputational crisis,
- the ability to work under time pressure,
- the ability to maintain consistent communication across multiple channels,
- and the ability to work with technical teams and senior management.
It is precisely these skills that ensure communication does not exacerbate the incident, but instead helps the organisation to handle it in a mature manner.
Summary: communication readiness is part of cyber resilience
An organisation prepared for a data breach is not just one with a good SOC, security procedures and an incident response plan. It is also an organisation that knows:
- whoever says,
- whatever says,
- whenever says
- to whom speak
- and how to maintain trust in a situation of high uncertainty.
For PR and marketing departments, this means they need to get involved in the conversation about cybersecurity much earlier – not when things are already in crisis, but at the planning stage.
Because, in practice, the crisis following a data breach unfolds simultaneously on two levels:
- technical,
- and reputational.
If a company isn’t prepared for the latter, it’s very easy to fail despite having done a good job on the operational side.